Table of Contents
DPDP Act Explained for Chartered Accountants:
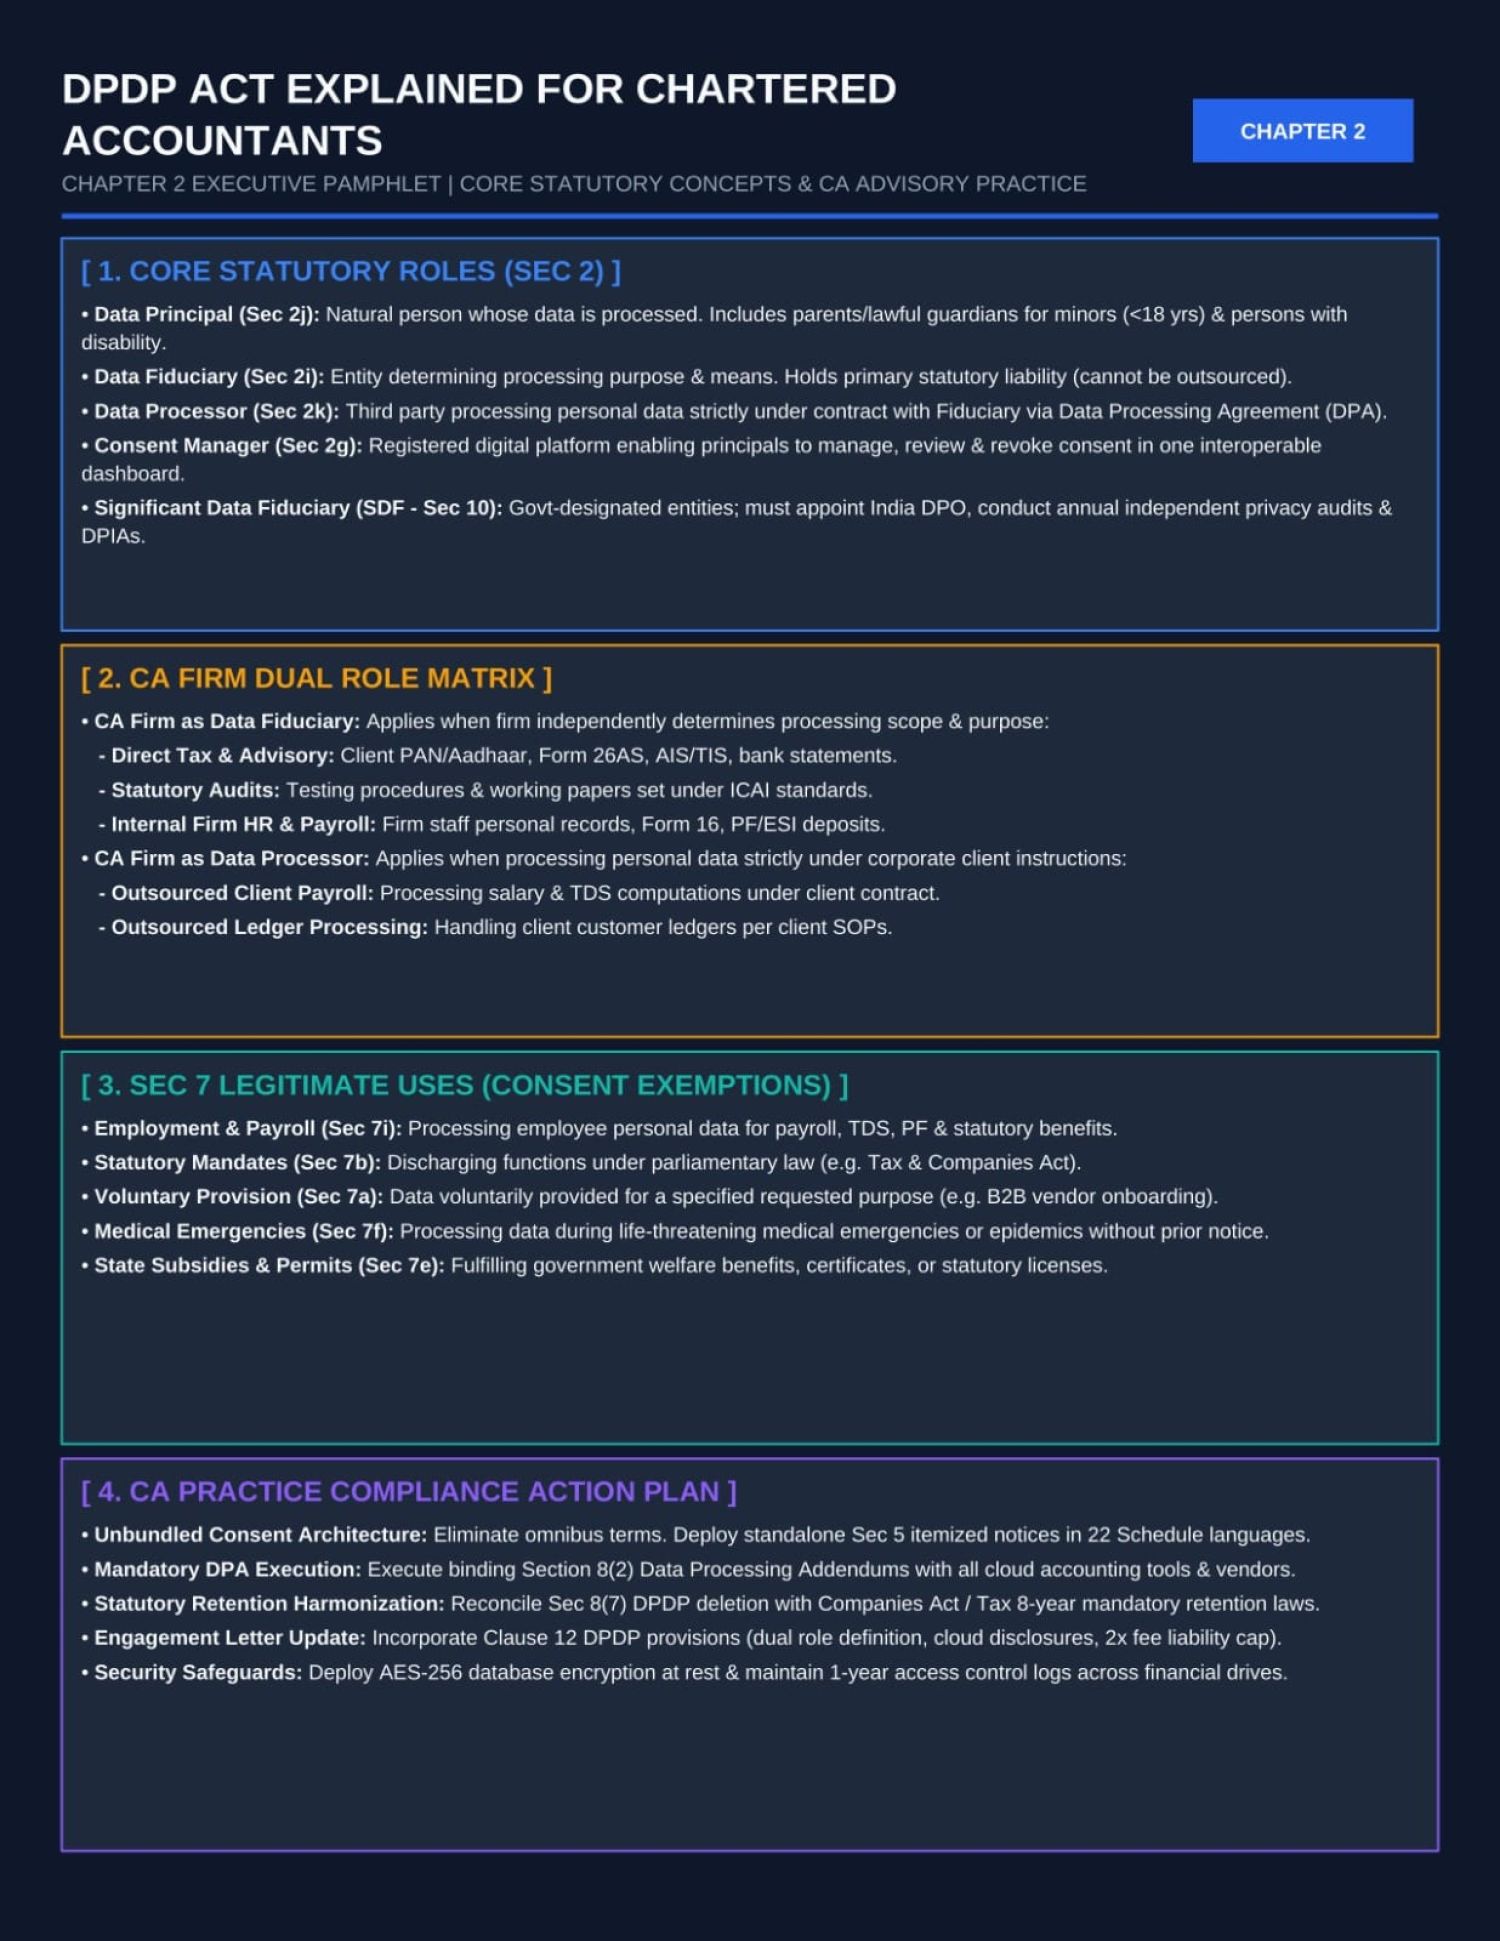
Here we explain how the Digital Personal Data Protection (DPDP) Act, 2023, applies specifically to Chartered Accountants (CAs), CA Firms, Tax Consultants, Auditors, and Professional Service Firms. The main message is that a CA firm can act either as a data fiduciary or a Data Processor, depending on the nature of the engagement.
1. Core Statutory Roles (Section 2):
The DPDP Act defines several key stakeholders.
A. Data Principal [Section 2(j)]: A data principal is the individual whose personal data is being processed. Examples like client, employee, director, shareholder, debtor, creditor, and vendor. Special Cases For Children Below 18 Years, Persons With Disabilities. their lawful guardians exercise rights on their behalf.
Rights of Data Principal: They can know what data is collected, request access, seek correction, update information, request deletion (where legally permitted), and File grievances. Example for CA Practice: A client provides PAN, Aadhaar, bank account details, and income details. The client becomes the data principal.
B. Data Fiduciary [Section 2(i)] : A data fiduciary is the entity deciding Why data is collected, How it is processed. Important Principle: "Primary statutory liability cannot be outsourced." This means even if a CA firm uses Cloud storage, Payroll software, tax filing platforms, and outsourced IT vendors, the responsibility remains with the data fiduciary. Example: A CA firm decides which client documents to collect How long records will be retained, and Which software will store data. The CA firm acts as a data fiduciary.
C. Data Processor [Section 2(k)]: A Data Processor processes personal data on behalf of a Data Fiduciary. They do not decide Purpose, Means They merely follow instructions. Examples: payroll service providers, Cloud storage providers, software vendors, and bookkeeping BPOs
- Requirement : Processing must occur under a formal:
- Data Processing Agreement (DPA) : The DPA should define the scope of processing, security requirements, confidentiality obligations, and Deletion requirements
D. Consent Manager [Section 2(g)]: A Consent Manager is a registered entity that helps individuals Give consent, track consent, withdraw consent, and review permissions through a common dashboard. Example: Similar to a privacy management portal where a person can see Which organizations have access to their data, which permissions are active and How to revoke them.
E. Significant Data Fiduciary (SDF) [Section 10]
The government may classify some organizations as significant data fiduciaries.
Factors Considered : Volume of data processed, Sensitivity of data, Risk to citizens and Impact on national interests.
Additional Obligations:
- Appointment of DPO : (Data Protection Officer) Must Be based in India and the Handle compliance matters.
- Independent Audits : Annual privacy audits become mandatory.
- DPIA Data Protection Impact Assessment to evaluate privacy risks.
2. CA Firm Dual Role Matrix:
This is one of the most important concepts for CA professionals. A CA firm may play two different legal roles.
A. CA Firm as Data Fiduciary: This applies when the CA firm independently decides how personal data will be processed.
- Direct Tax & Advisory: The firm collects PAN, Aadhaar, Form 26AS, AIS/TIS, and Bank statements. The firm determines the information required, processing methods, and storage mechanisms. Therefore, CA Firm = Data Fiduciary
- Statutory Audit: During audit The CA firm collects employee data, vendor information, director records, and financial documentation. The audit approach, testing procedures, and working papers are determined by ICAI standards. Therefore, CA Firm = Data Fiduciary
- Internal Firm HR and Payroll: The firm processes employee records, Form 16, PF information, ESI information and Salary details. The firm decides the purpose. Therefore, CA Firm = Data Fiduciary
B. CA Firm as Data Processor: This occurs when the firm merely acts on client instructions.
- Outsourced Client Payroll: Example: A company outsources payroll processing. The CA firm calculates salary, computes TDS, and Generates payroll reports. The client decides why data is processed. Hence: Client = Data Fiduciary and CA Firm = Data Processor
- Outsourced Ledger Management: The client instructs Maintain sales ledger and Prepare customer accounts. CA firm processes customer information according to client SOPs. Hence, Data Processor. Practical Example: Suppose a company hires your CA firm.
- Tax Planning Assignment: You determine required documents, tax strategy, and processing activities, which Result: Data Fiduciary
- Payroll Processing Assignment: The client determines the employee list, salary structure, and HR policies. You merely process. Result: Data Processor
3. Section 7 Legitimate Uses (Consent Exemptions):
The DPDP Act allows certain processing without consent.
A. Employment & Payroll: Consent is not required for salary processing, PF deductions, ESI deductions, Bonus calculation and TDS deductions. Example: An employer does not need to obtain fresh employee consent every month to process payroll.
B. Statutory Mandates: Consent is not required when processing is necessary to comply with law. For Examples
- Income Tax Act: TDS filings, ITR filings
- Companies Act: Annual Return and Financial Statements
- GST Law: GST returns, E-way compliance
- Insolvency & Bankruptcy Code: CIRP disclosures, claim processing, and Committee of Creditors records. As an RP or Liquidator, much data processing falls under statutory obligations.
C. Voluntary Provision: If a person voluntarily provides information for a specific purpose: Consent may not be separately required. Example: A prospective client emails, "Please review my tax position." The firm can use the information to perform that requested service.
D. Medical Emergencies: Processing without consent is permitted where necessary for medical emergencies, epidemics, and life-threatening situations.
E. State Subsidies and Licenses: Government authorities may process personal data for welfare schemes, subsidies, licenses, and certificates without seeking separate consent.
4. CA Practice Compliance Action Plan
CA firms, what practical steps should be taken?
A. Unbundled Consent Architecture: In this case, it advises avoiding broad and vague consent and instead providing specific notices. Example: Separate notices for tax filing, audit services, payroll processing, and marketing communications. This improves transparency.
B. Mandatory DPA Execution: Execute Data Processing Agreements with cloud vendors, payroll software vendors, document storage providers, and accounting software providers. This is objective. To clearly define responsibilities, Data security measures, and liability allocation
C. Statutory Retention Harmonization : One major challenge for CAs is record retention.
- DPDP Principle: Delete personal data when no longer necessary.
- Other Laws Require Retention: Examples: Income tax records: often retained for several years, company act records, audit working papers, and GST documents. A documented retention schedule must reconcile these requirements.
D. Engagement Letter Update: The company needed to update engagement letters. Include:
- Role Clarification: Specify whether the firm acts as Data Fiduciary and Data Processor
- Cloud Hosting Disclosure: Specify where data is stored and which third parties are involved
- Liability Clauses: Clearly define risk allocation, indemnities, and limitation of liability
E. Security Safeguards:
- AES-256 Encryption: Protect databases containing PAN, Aadhaar, bank details, and tax information.
- One-Year Access Logs: Maintain records showing who accessed data, when access occurred, and What changes were made. This supports investigations, audit trails, and regulatory compliance
Key Learning for Chartered Accountants and Insolvency Professionals
For professionals such as CAs, Insolvency Professionals (IPs), Resolution Professionals (RPs), and Liquidators, the most important takeaway is:
- Understand Your Role: For every engagement, identify whether you are a data fiduciary or a data processor
- Use Section 7 Exemptions Properly: Many professional activities such as payroll processing, tax compliance, statutory filings, and IBC-related disclosures may be carried out under legitimate use provisions without obtaining fresh consent.
- Strengthen Documentation: Maintain privacy notices, engagement letters, Data Processing Agreements (DPA), retention schedules, and incident response procedures
- Improve Data Security: Implement encryption, role-based access controls, secure backups, access logs, and vendor oversight. In short, this chapter translates the DPDP Act into a practical compliance roadmap for CA firms and professional practices, showing when a firm is legally responsible for data and what controls must be implemented to avoid regulatory and reputational risks.